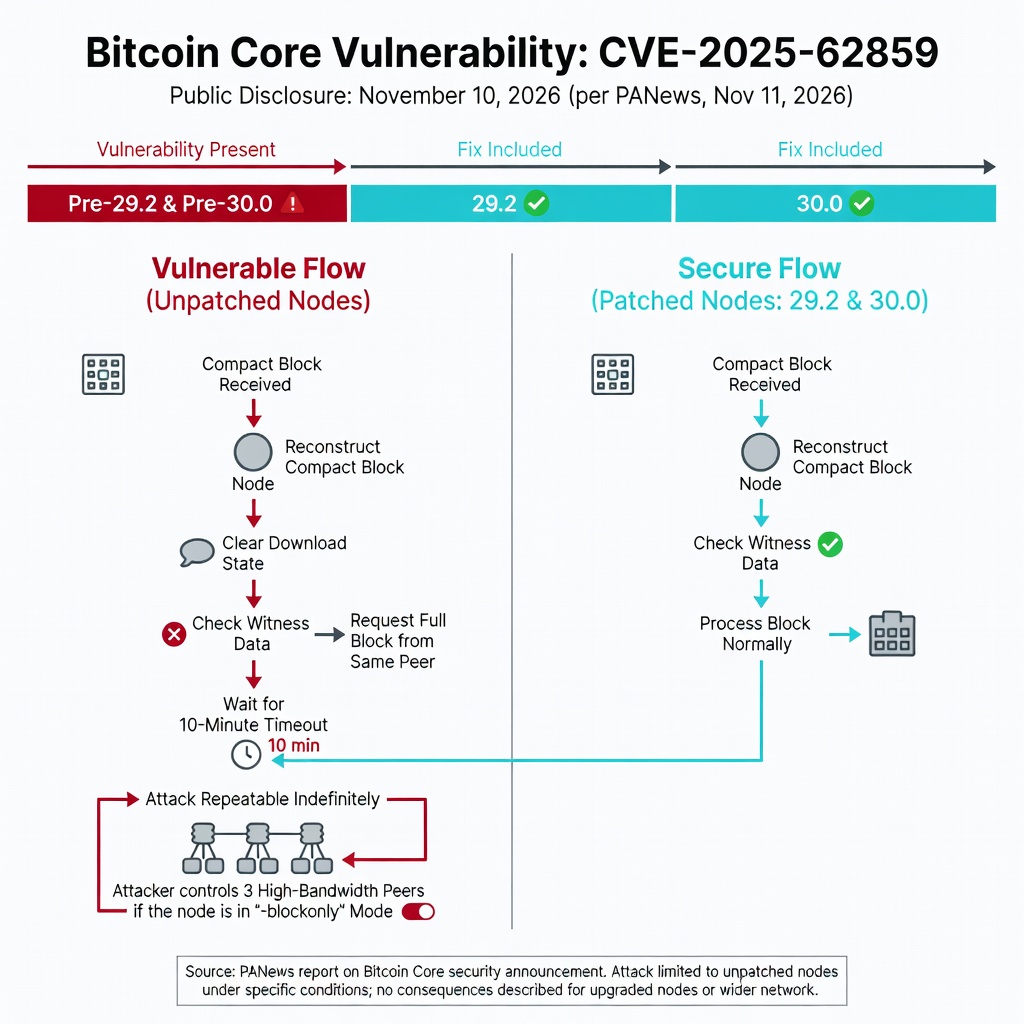
On November 10, 2026, Bitcoin Core publicly disclosed medium-severity vulnerability CVE-2025-62859, according to a PANews report published on November 11, 2026. The issue is present in versions before 29.2 and 30.0, and the fix is included in those releases.
Witness malleation in compact blocks
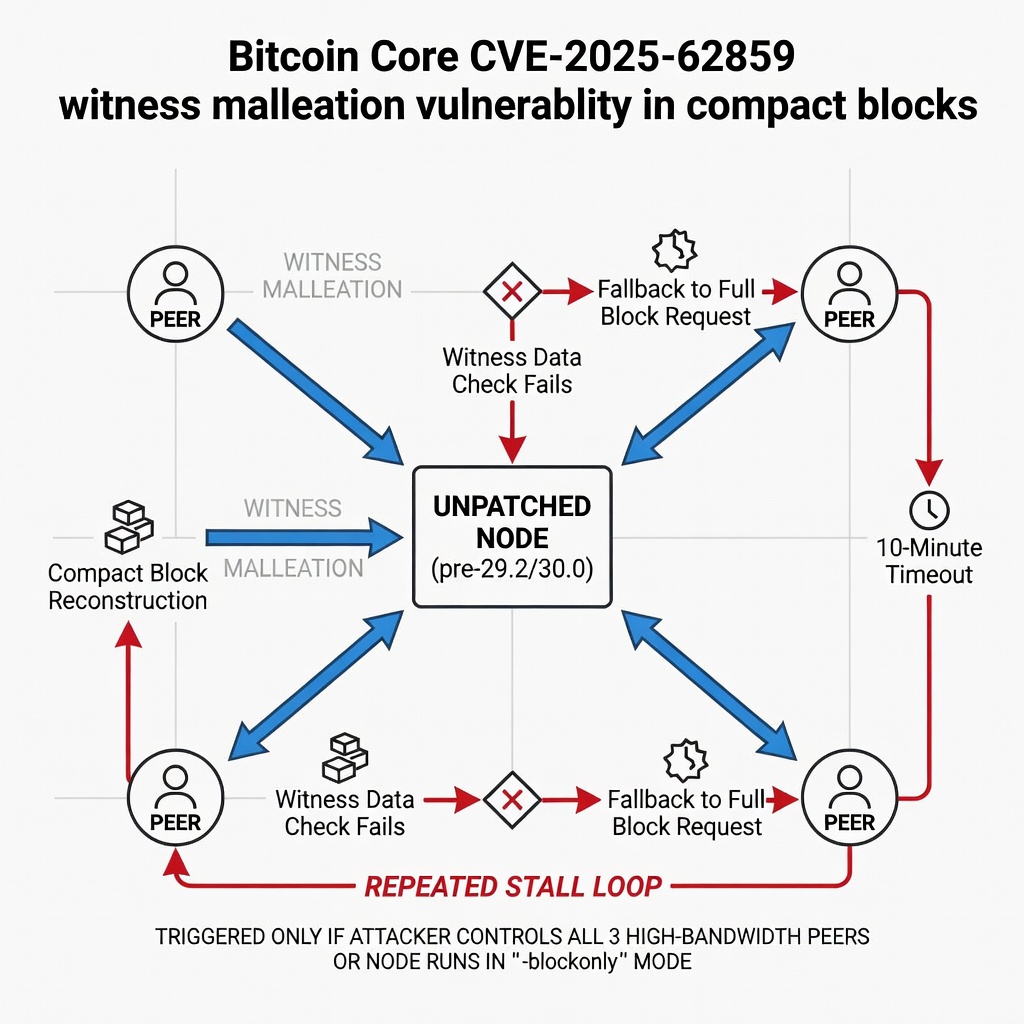
A malicious node can use witness-data tampering, described as witness malleation, inside compact blocks to stall a victim’s block processing under specific conditions.
The Bitcoin Core security announcement states that an affected node clears its download state after reconstructing a compact block and before checking the witness data. If that check fails, the node falls back to requesting the full block from the same peer and waits for a 10-minute timeout.
When the stall can be repeated
The announcement says the attack can be repeated indefinitely if the attacker controls the victim’s three high-bandwidth peer nodes, or if the victim is running in -blockonly mode. The reported effect is limited to unpatched nodes that meet one of those conditions; the source does not describe consequences for upgraded nodes or for the wider network.