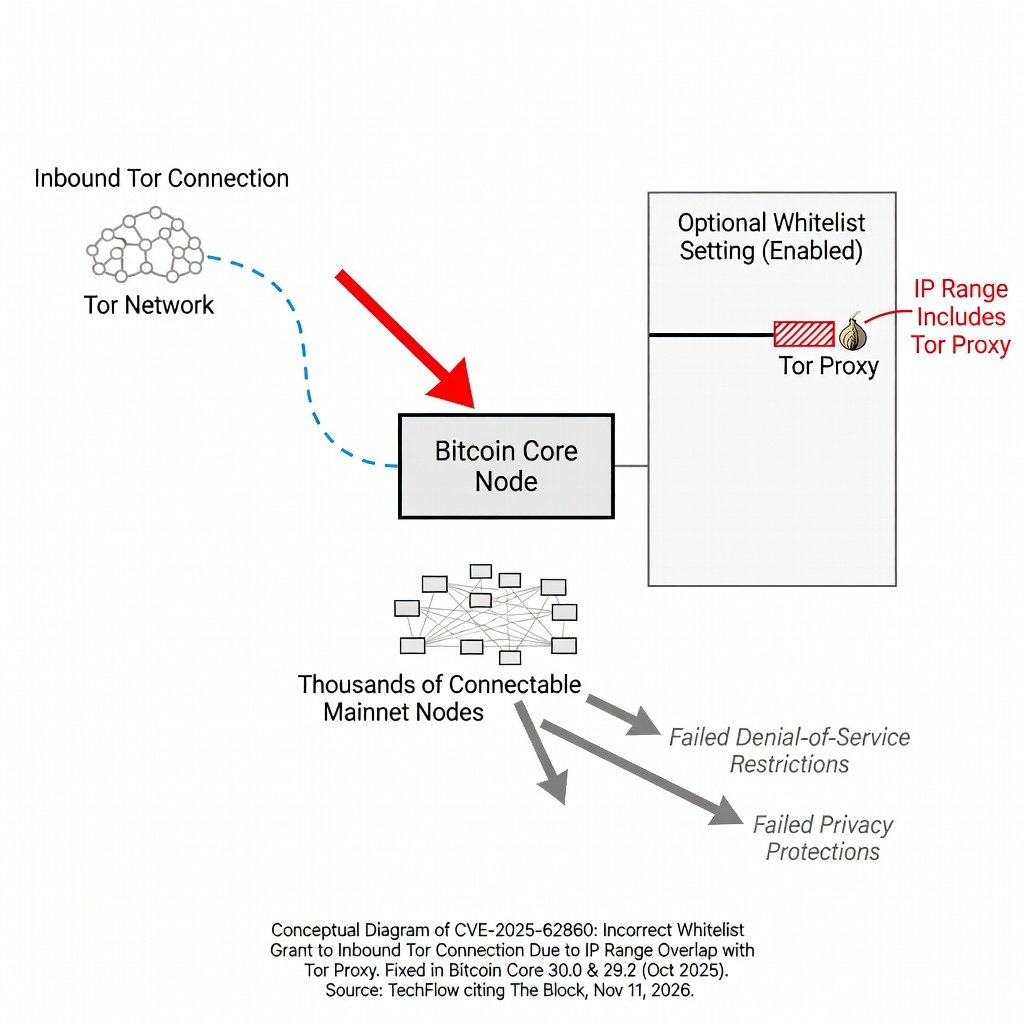
On November 11, 2026, TechFlow reported, citing The Block, that Bitcoin Core disclosed an already-fixed medium-severity vulnerability. Under specific configurations, a node could incorrectly grant whitelist permission to an inbound Tor connection.
The issue is CVE-2025-62860. It affects nodes that enabled the optional whitelist setting and whose IP range includes the Tor proxy. Bitcoin Core said thousands of connectable mainnet nodes had whitelisted inbound Tor connections, so some denial-of-service limits and privacy protections did not apply.
Fixes were already included in Bitcoin Core 30.0 and 29.2 in October 2025. Two other vulnerabilities disclosed in the same period, covering block processing and block-template creation by mining nodes, were reported separately by TechFlow earlier.
What the report attributes to Bitcoin Core
Bitcoin Core’s statement, as relayed by TechFlow via The Block, limits the described exposure to those whitelisted inbound Tor connections on connectable mainnet nodes. The report gives the scale only as thousands of such nodes and describes the effect as the failure of some denial-of-service restrictions and privacy protections.
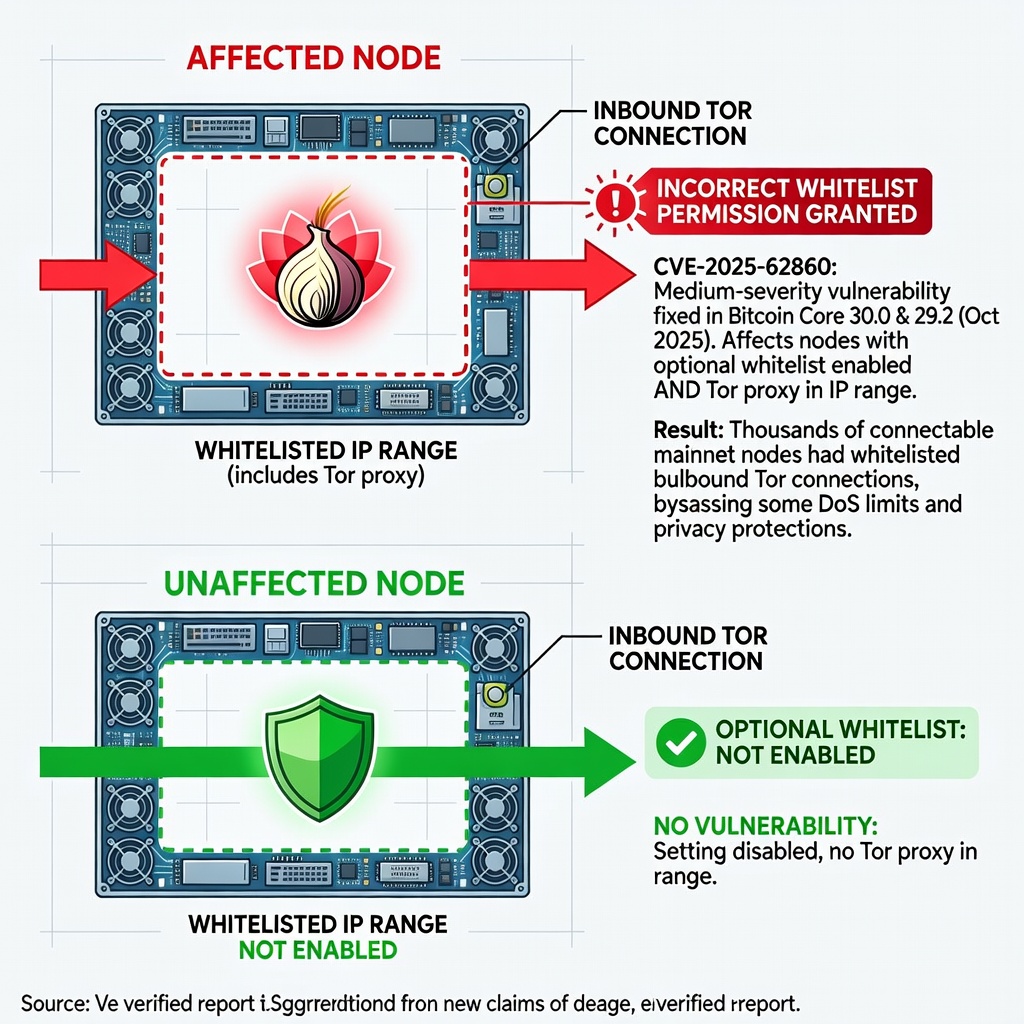
Configuration boundary
The vulnerability is described only for nodes that turned on the optional whitelist and whose whitelist IP range contains the Tor proxy. The report does not say that nodes without that setting were affected.
TechFlow original report (published November 11, 2026, 20:52 +08).