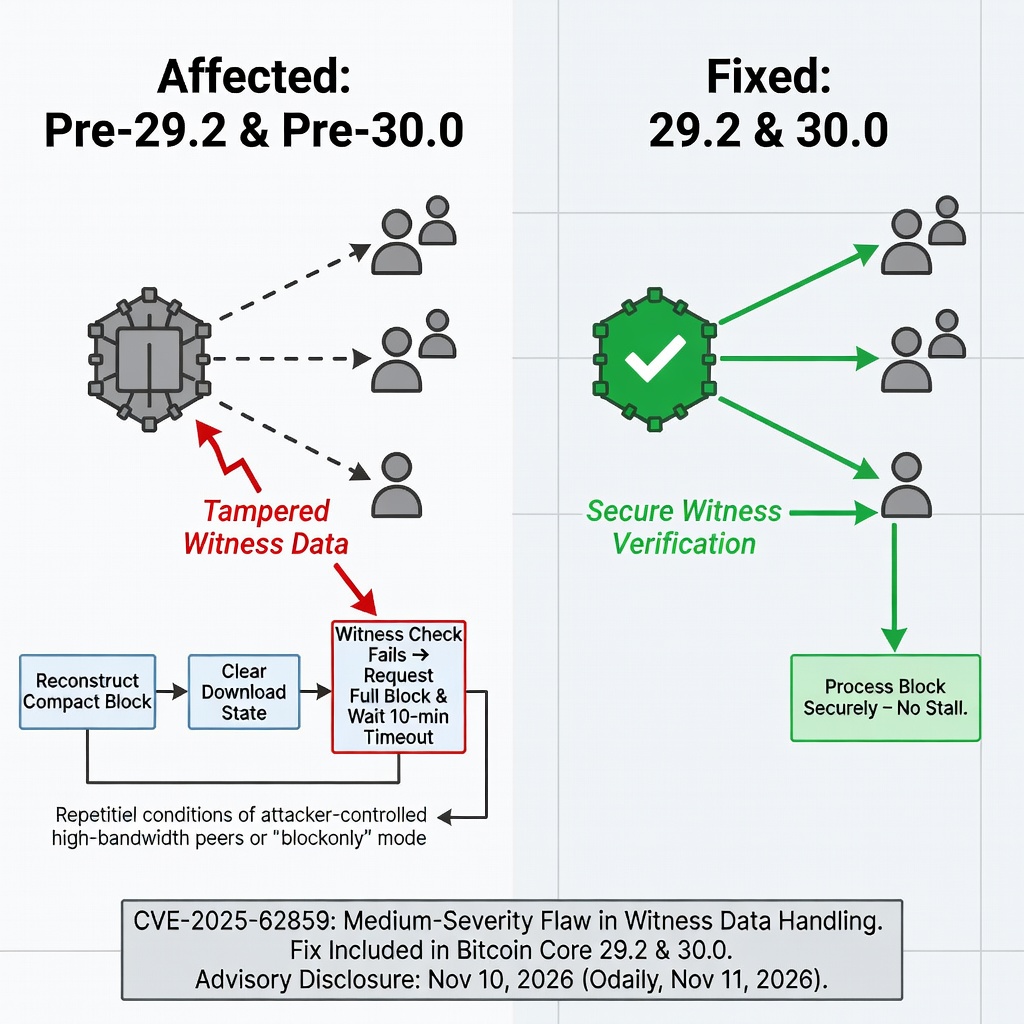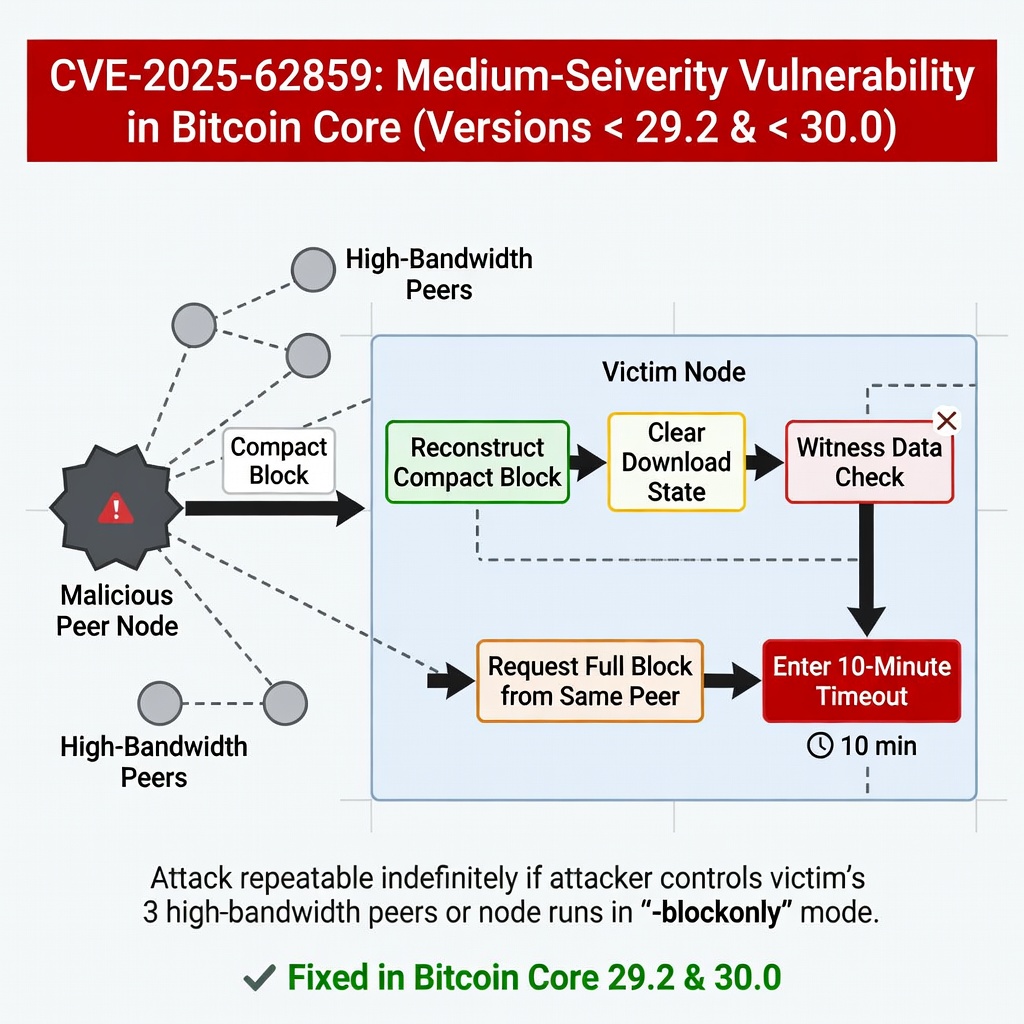
On November 10, 2026, a Bitcoin Core security advisory publicly disclosed the medium-severity vulnerability CVE-2025-62859, according to an Odaily news flash published on November 11, 2026. The flaw is present in versions before 29.2 and 30.0. A malicious node can tamper with witness data inside a compact block and, under specific conditions, stall the victim node’s block processing.
How processing stalls
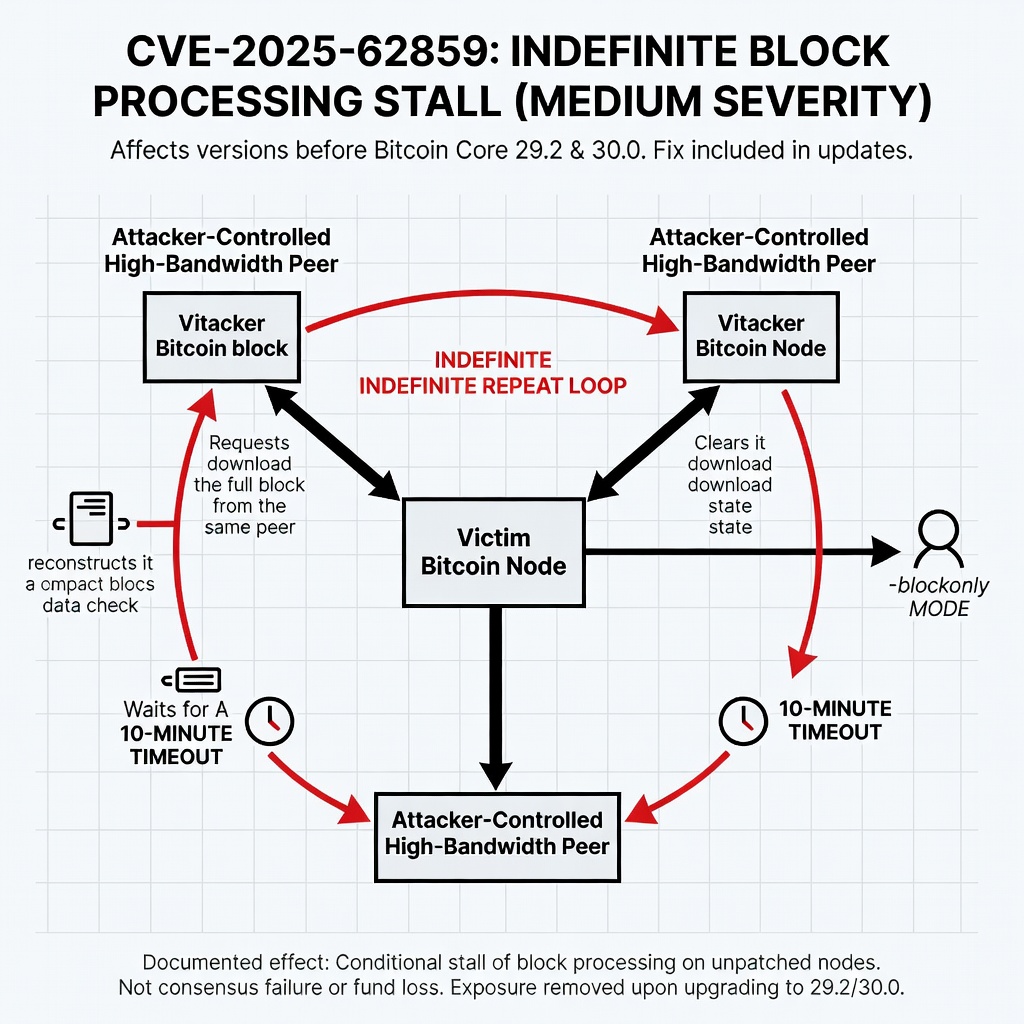
After an affected node reconstructs the compact block, and before it checks the witness data, it clears its download state. If the witness check then fails, the node requests the full block from the same peer and waits for a 10-minute timeout.
When the stall can be repeated
Odaily’s report of the advisory states that the attack can be repeated indefinitely if the attacker controls the victim’s three high-bandwidth peers, or if the victim is running in -blockonly mode. The fix is included in Bitcoin Core 29.2 and 30.0.
What this does and does not establish
The documented effect is a conditional stall of block processing on unpatched nodes, not a claim of consensus failure or loss of funds. The report does not quantify how many nodes remain on affected releases, how often an attacker can hold the required peer positions, or how long any stall would persist on the wider network. Any outlook implication is therefore limited to operators still below 29.2 and 30.0: processing can be delayed if those peer or -blockonly conditions are met, and that exposure is removed once the fixed releases are in use. No broader propagation or market conclusion is supported by the flash.
Source: Odaily news flash, published November 11, 2026 (advisory disclosure dated November 10, 2026).